CAC/PIV is used by U.S. Federal Agencies and Federal Contractors.
CAC/PIV e-signature authentication is available on Enterprise Plus and Enterprise Advanced plans only and requires customers to be provisioned on the Box Sign CAC/PIV Add-On Pack.
Card-specific limitations that we do not support include:
Cards with no digital signing capability
Unsupported digital signature algorithms (Box supports RSA and ECDSA)
Expired certificate
U.S. Government organizations require additional security measures to safeguard critical information and data. Common Access Cards (CAC) are identification cards that are issued to U.S. Department of Defense personnel. These cards enable physical access to buildings and provide access to DoD computer networks and systems. While CAC cards are the primary identification cards for DoD personnel, Personal Identification Verification cards (PIV) are smartcards used by other branches of the U.S. Federal Government that contain a certificate and a private key to gain access to computers, networks, and online resources. With Box Sign, these organizations can enable and require signature request recipients to authenticate themselves using their CAC or PIV smartcards before gaining access to signing Box Sign signature requests.
To ensure a seamless signing experience, Box Tools must be installed for each user receiving signature requests requiring CAC/PIV authentication. This step is crucial to enabling CAC/PIV for your organization.
Compatibility requirements for using CAC/PIV with Box Tools:
CAC/PIV smartcard
Operating system: Windows 10, Windows 11, or macOS
Box Tools: Version 4.31 or above
Visit Installing Box Tools for further instructions and how to install Box Tools.Once complete, recipients can then authenticate themselves using CAC/PIV hardware.
After adding recipients to a signature request, select which recipient to modify, and select the CAC/PIV option within the Additional Recipient Authentication dropdown menu.Multiple signers with CAC/PIV authentication can be added to the same signature request:
Each CAC/PIV signer authenticates independently using their own CAC/PIV smartcard.
CAC/PIV signers can be positioned in any order within the signing sequence.
CAC/PIV authentication can be used for some signers, while other recipients in the same signature request can be assigned other authentication methods (SMS, password, Box Login).
Senders must either set a signing order manually or use automatic ordering before sending the signature request.
Long-term validation for CAC/PIV signatures is not enabled.
Digital signatures are stripped upon any upload of a signed document into a Box Sign signature request. For example, a sender has a document that requires the signature of two signers, but the document has already been signed by one of those signers who completed the signing process (either through Box Sign or another signing platform). The sender then uploads that executed document to Box Sign in a separate signature request to obtain the second signature. Box Sign will strip the pre-existing digital signatures from the document (the prior signer’s CAC/PIV signature and the Box platform digital signature tamper seal), to allow Box Sign to apply the CAC/PIV signature of the second signer and the Box platform digital signature tamper seal. The CAC/PIV digital signature of the first signer cannot be reinstated in the document.
The sender can require an added password for the recipient with CAC/PIV. The recipient will first enter a password before proceeding with the CAC/PIV authentication. SMS authentication is not available (Box login is required with CAC/PIV, see Additional recipient authentication).
After a signer begins the signature request process, neither the sender, nor any other user who the signature request is shared with and has access to revise the request, can revise the request for that signer. However, the sender, or any other user who the signature request is shared with and has access to revise the request, can revise the request as described in Changing a sent signature request, including updating the CAC/PIV settings, before the signature request process begins.If a signature request doesn’t have a signing order, the sender cannot add CAC/PIV signers when revising the request.
Box Tools must be installed on your computer before enabling CAC/PIV. The recipient will be presented with an error during the authentication process if Box Tools is not installed.
As the recipient starts the signing process, click Review document from the email request.Once a recipient initiates a signature request, they will be required to authenticate with CAC/PIV.
After a successful connection, the signer will need to select the appropriate CAC/PIV card from the drop-down menu.
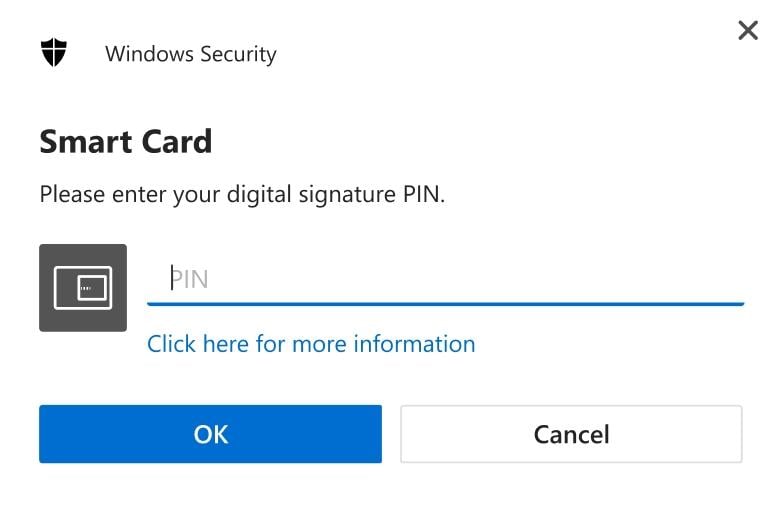
After completing the authentication process, the signer follows the steps in Signing a document, and then after clicking Sign & Finish before submitting the signature, the signer will need to enter a PIN to complete the process.
The recipient’s selection is recorded in their signature block or initials field within the signed document and in the signing log for reference.
Once the signature request is complete, the signing log is available for review and reference. The signing log displays each CAC/PIV signature and authentication details as pictured below. You can learn how to access the signing log associated with each signature request here.
For additional information about how Box can support compliance with CAC/PIV, contact your account manager or client success manager.
Last modified on September 11, 2026
Was this page helpful?
Assistant
Responses are generated using AI and may contain mistakes.